
Ready for worry-free infrastructure?
Share your hosting setup, cloud provider, deployment flow, and failure points. We’ll map a safer infrastructure path with monitoring, backups, and release control.
Cloud Infrastructure & DevOps
Stop losing sleep over server crashes
Your infrastructure should be invisible, not a constant source of anxiety. We design, build, and manage cloud systems that deploy automatically, scale effortlessly, and alert you before problems become outages.
Where infrastructure starts blocking the business
Most teams lose sleep over infrastructure. Slow deployments, surprise downtime, runaway cloud bills, and security gaps create constant anxiety. When something breaks at 2 AM, nobody knows how to fix it.
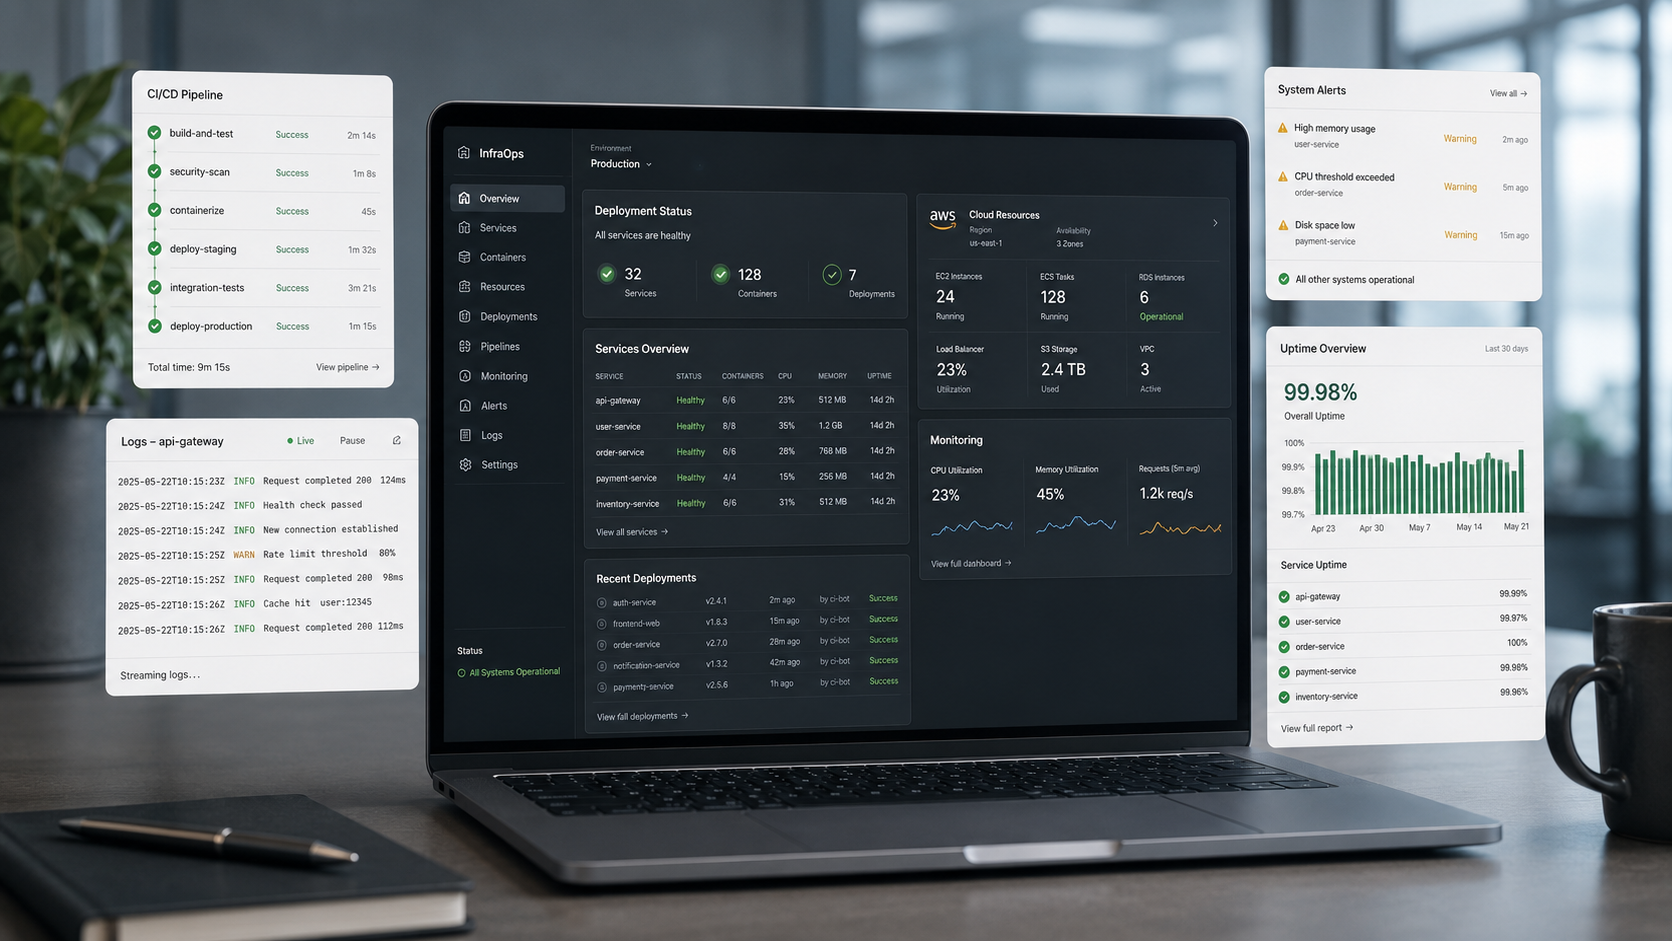
Cloud systems built for stable releases, clean operations, and fewer surprises
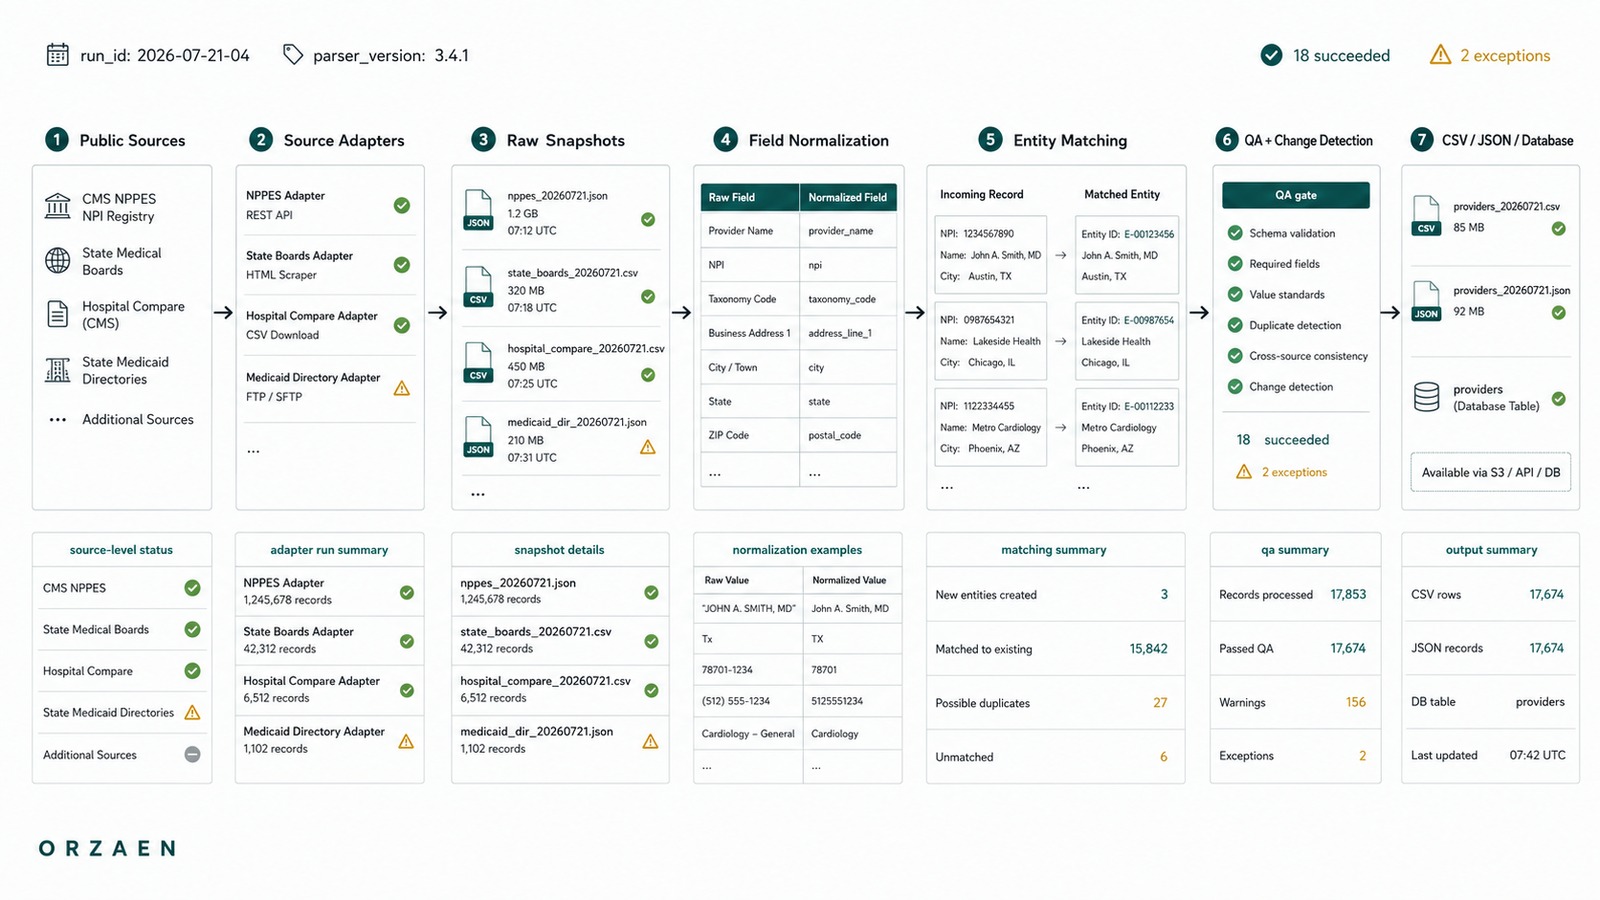
Orzaen designs, builds, and manages cloud infrastructure that just works. We set up automated deployments, monitoring, backup systems, and security controls so your team can ship code without worrying about what happens underneath.
We use Infrastructure as Code, containerization, and CI/CD pipelines to create reproducible, scalable environments. Whether you need a simple deployment setup or a multi-region architecture, we build infrastructure that grows with your business.
Client Feedback
“Wonderful to work with, knowledgable and kind! Great work!”
Karah S. / CRM Operations Manager, MarketSurge User
Infrastructure Barriers We Remove
The failure points that usually show up after launch
We turn risky deployments, unclear server ownership, weak backups, missing alerts, cost drift, access gaps, and scaling problems into infrastructure your team can operate with confidence.
Deployment
Every release feels risky
Our Solution
Controlled CI/CD paths reduce manual production changes
Downtime
Servers fail before the team notices
Our Solution
Monitoring, uptime checks, and alerts make failures visible early
Recovery
Backups exist but restore steps are unclear
Our Solution
Backup rules and recovery notes make incidents easier to handle
Security
Ports, credentials, and access rules are loosely managed
Our Solution
IAM, secret handling, WAF rules, and environment separation reduce exposure
Scaling
Traffic spikes turn into emergency work
Our Solution
Load balancing, health checks, and scaling rules prepare the system
Cost
Cloud spend grows without clear ownership
Our Solution
Resource review and right-sizing reduce waste without weakening the system
Operations
Infrastructure knowledge lives in one person’s head
Our Solution
Runbooks, architecture notes, and handoff docs make operations repeatable
Visibility
Logs, metrics, and alerts are scattered across tools
Our Solution
Central dashboards and alert routes help teams debug faster
Services
Infrastructure and DevOps work we build around real operational risk
Cloud Architecture Design
Multi-region, multi-AZ architectures with auto-scaling, load balancing, CDN integration, and disaster recovery. We design for your current needs with clear upgrade paths as you grow. Support for AWS, GCP, and Azure.
Infrastructure as Code
Terraform, Pulumi, and CloudFormation templates that version-control your entire infrastructure. Reproducible environments, automated drift detection, and seamless team collaboration. No more manual console clicks.
CI/CD Pipeline Setup
Automated build, test, and deployment pipelines with GitHub Actions, GitLab CI, or AWS CodePipeline. Feature branch previews, automated rollbacks, and deployment approval gates. Ship code with confidence.
Containerization & Kubernetes
Docker containerization with Kubernetes or ECS orchestration. Auto-scaling, rolling updates, service discovery, and health checks. From first container to production cluster.
DevOps Monitoring & Support
Prometheus and Grafana dashboards, centralized logging with ELK/Loki, PagerDuty incident management, and 24/7 on-call rotation setup. Proactive alerting before issues impact users.
Use Cases
Where stable infrastructure removes daily firefighting
Infrastructure Results
Proof from cloud, deployment, and automation work that had to hold up
Platforms We Work With
Cloud providers, deployment tools, databases, and monitoring systems we connect into one stable setup.
Source Registry
AWS
Approach
Multi-AZ deployments with EC2, ECS, or EKS. RDS for managed databases. S3 for storage. CloudFront for CDN. CloudWatch for monitoring. Cost optimization with reserved instances and Spot.
Output
Production-grade AWS infrastructure with auto-scaling, backups, and monitoring.
Examples
EC2, ECS, EKS, Lambda, RDS, S3, CloudFront, Route 53
Architecture View
Infrastructure layers before production deployment
We map the public entry point, application runtime, data layer, and monitoring path so the system is easier to deploy, operate, and recover.
Edge
Public entry layer for DNS, CDN, SSL, WAF protection, routing, and load balancing.
Cloudflare · Route 53 · WAF · SSL · Load Balancer
Application
Runtime layer for APIs, containers, workers, compute services, and scaling rules.
ECS / EKS · Lambda · API Gateway · Auto-Scale · Service Mesh
Data
Persistence layer for databases, cache, storage, backups, replicas, and restore paths.
RDS Cluster · Redis Cache · S3 Storage · Backups · Read Replica
Observability
Visibility layer for metrics, logs, traces, alerts, dashboards, and incident response.
Prometheus · Grafana · Logs · PagerDuty · Tracing · Alerts
99.9%
Uptime SLA
<15 min
Incident Response
Daily
Backups
Security & Recovery Checklist
Infrastructure review points before handoff
Risky deployment
- ×Build depends on a local machine
- ×Files are moved by hand
- ×Environment variables are changed manually
- ×Database changes are applied directly
- ×Services are restarted without checks
- ×Production is used for verification
- ×Rollback depends on backup restore
With Orzaen control
- ✓Code change starts the pipeline
- ✓Build and checks run first
- ✓Container or artifact is created
- ✓Staging receives the release
- ✓Health checks confirm readiness
- ✓Production switch follows release rules
- ✓Rollback path is already defined
Deployment Control
Stop treating every release like a risk.
We replace fragile manual deployments with a controlled release path your team can repeat, monitor, and recover from.
Every deployment should have a known path, known rollback, and visible health state after release.
Cloud & DevOps Stack
Built with tools for deployment, monitoring, security, and recovery
We choose cloud platforms, container tools, databases, CI/CD systems, monitoring, storage, and access controls based on your workload and the operational risks your setup needs to handle.
01
Cloud Platforms
Hosting, networking, managed services, storage, and production environments selected around workload needs.
02
Compute & Containers
Application runtimes, containers, workers, queues, scaling rules, and service orchestration.
 Docker
03
Deployment Flow
Build pipelines, release steps, environment variables, approval gates, rollback paths, and repeatable deployment automation.
 GitHub Actions
04
Data Layer
Databases, cache, object storage, backups, restore paths, and persistence layers behind production systems.
 PostgreSQL
 MongoDB
 Redis
 S3
05
Monitoring & Alerts
Uptime checks, logs, metrics, dashboards, error tracking, alerting, and operational visibility for live systems.
 Sentry
06
Security & Edge
DNS, SSL, CDN, firewall rules, access controls, secrets, encryption, and protection around public services.
Delivery Workflow
How we move from unstable infrastructure to controlled operations
We audit the current setup, design the target architecture, build the infrastructure, automate deployment, add monitoring and recovery, then hand over a system your team can operate.
Audit the current setup
We review hosting, cloud provider, servers, DNS, databases, deployments, backups, alerts, access rules, and the failure points causing risk.
Design the target architecture
We map the traffic path, compute layer, data layer, security rules, deployment flow, monitoring, and recovery approach.
Build the infrastructure
We configure servers, containers, databases, storage, networking, secrets, cloud services, and infrastructure code.
Automate deployment
We set up CI/CD, build steps, environment handling, release rules, rollback paths, and deployment checks.
Add visibility and recovery
We connect logs, metrics, alerts, uptime checks, backups, restore notes, and incident visibility so the system can be operated safely.
Handoff with runbooks
We document how the system works, how to deploy, what to monitor, where risks live, and what to do when something fails.
Controlled Workflow
Each step connects hosting, DNS, compute, storage, databases, CI/CD, secrets, backups, logs, alerts, and recovery rules into one controlled infrastructure workflow.
FAQ
Questions clients ask before changing infrastructure
Still have questions? We typically respond within 2 hours.
Automation Field Notes
Lessons from building automation that runs in production
Request a Quote
Turn fragile infrastructure into a system your team can trust
Send your current hosting setup, cloud provider, deployment process, databases, traffic level, pain points, and failure history. We’ll review the safest path forward.
No perfect brief needed.
Project Brief